
Roughly 70% of the websites whose server-side language is known run on PHP, and this week a flaw that sat in its core for more than a decade became a working exploit with help from frontier AI, according to the researchers who found it. If you own a WordPress site, the patch is not optional, and it is not a WordPress update.
What is PHP2Shell?
On 21 October 2026, the PHP project released fixes for two critical flaws, CVE-2026-109618 and CVE-2026-109619. Both score 9.2 on CVSS v4.0, and allow an attacker to run code on a web server without logging in. The fixed versions are PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35. The problem lives in PHP itself rather than in WordPress, which is why WordPress.org confirmed that no WordPress update is required or planned. Wiz researchers showed unauthenticated code execution working against the latest official WordPress, Drupal, and Joomla container images at the time of testing.
The disclosure itself went sideways. Details leaked on 20 October right before the embargo. PHP brought its release forward by a day, and the UK National Cyber Security Centre advised organisations that cannot patch immediately to consider taking systems offline. Amazon’s honeypot network recorded an exploitation attempt on 17 October, four days before public disclosure, and watchTowr reports observing exploitation attempts. Huntress had not see in-the-wild exploitation across its partner base as of 21 October.
Where AI is the actor in this story
This is where the actual incident emphasised the headline version of this story. The researchers at Wiz, working with the PHP team, Calif, and OpenAI, say they used Wiz Atlas, Gemini 4 Argon, and GPT-5.6 Sol to find the flaws and build working exploits. Their claim is that one researcher completed in about a week with what would once have taken a world-class team months, and that the models let them develop, adapt exploits across several applications within hours. That is somewhat defenders using AI. On the attacker side, John Hammond of Huntress said the leak gave criminals an early warning window, and that they were undoubtedly using AI to find targets, and adapt exploits. That is an informed expectation, which no one wants to end up with finding out after its done.
So no, I cannot tell you that AI has been hacking the Internet since yesterday. What I can tell you is that AI has collapsed the effort between a hard bug, and a working exploit, and that is the shift every founder, business owner, and site owner needs to think through, upgrade reliable cybersecurity premiums, and much more — if it’s a very mature business that has been lagging behind digital, security and marketing transformations.
My Personal Anecdote
I have supported WordPress sites for years, and I have watched plenty of patch cycles come and go. Most felt like routine housekeeping. This is not the first big patch I have seen land, but it is the first where frontier AI sits at the centre of the story, at least from where I stand. That is why I think enterprises should treat it as a rehearsal to practice anticipations, and reactions when the time comes. Extra vigilance is now an operating cadence, and not to settle with some monthly reviews.
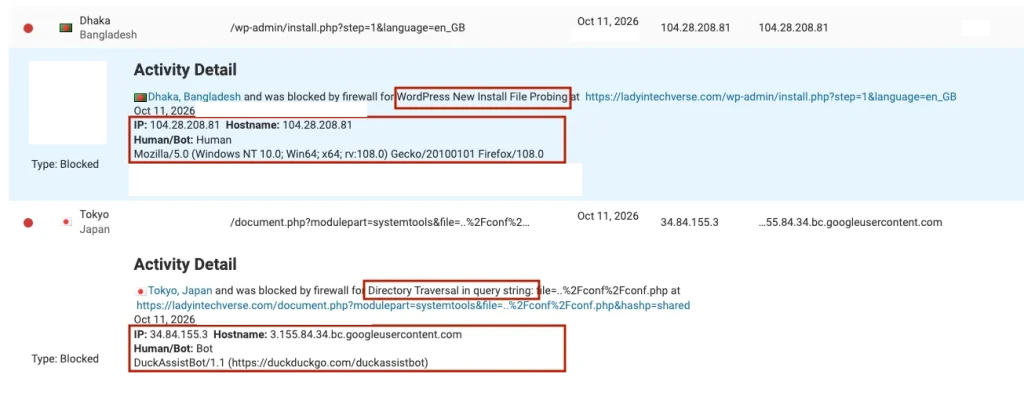
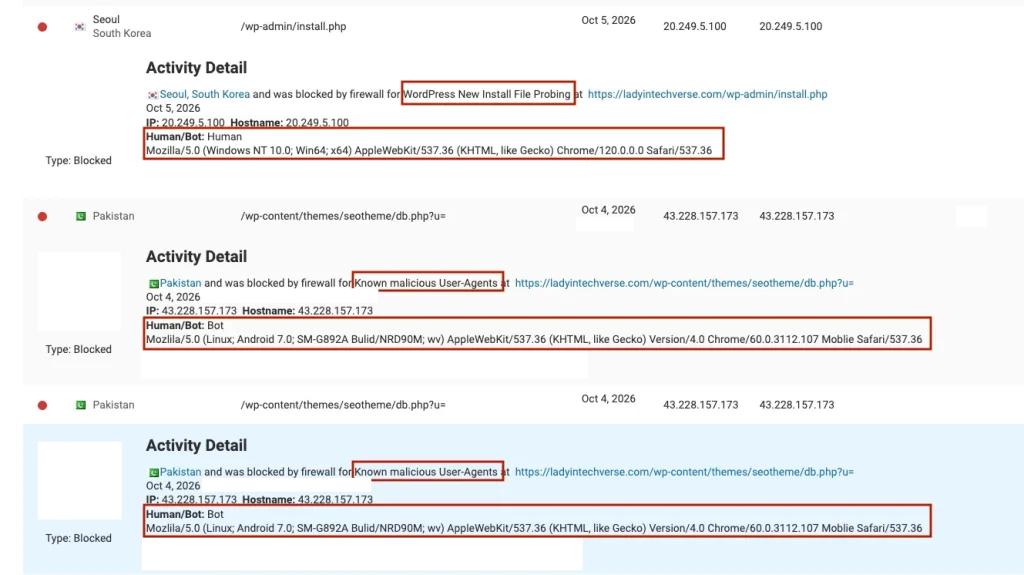
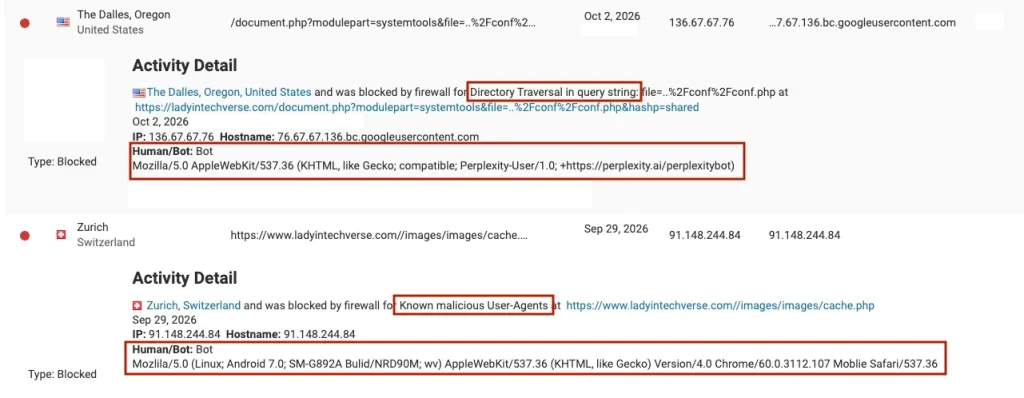
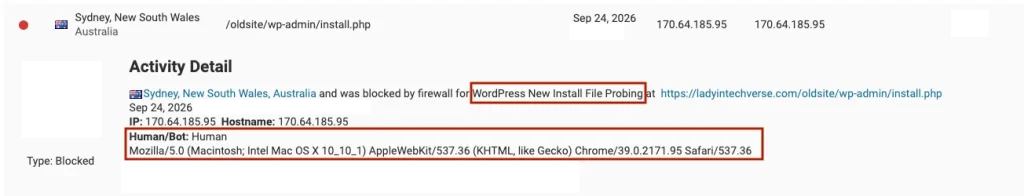
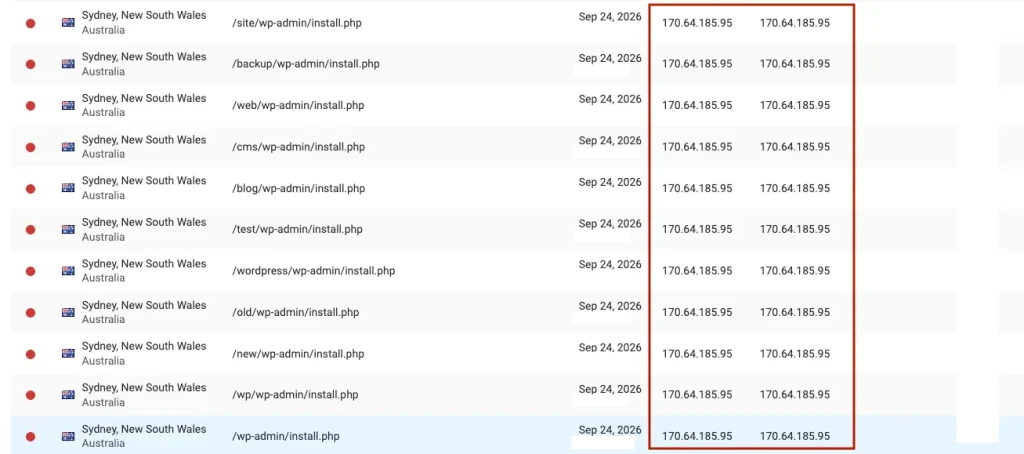
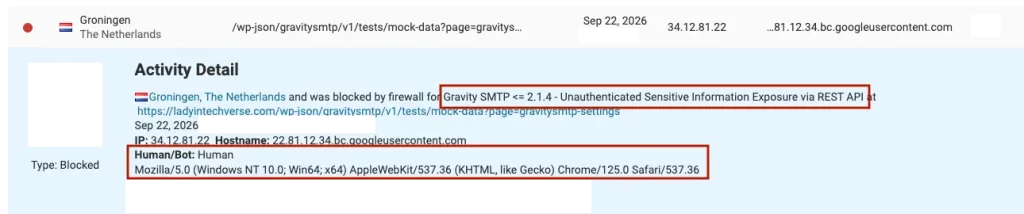
Here is where I am not pretending as a theorist. Between 22 September and 11 October 2026, my firewall logged automated probing from eight locations: Sydney, Seoul, Dhaka, Tokyo, Zurich, Groningen, The Dalles in Oregon, and Pakistan. Whoever these idiots are, they clearly have nothing better to do. One Sydney address tried /wp-admin/install.php under at least 12 different paths in about six seconds, hunting for a forgotten WordPress setup screen it could complete on its own terms. Others asked for files name /db.php and cache.php, the kind of names backdoors like to hide behind, or tried to climb the directory tree to read a configuration file. One went looking for a known flaw in an SMTP plugin. Every request in these screenshots are blocked by my firewall. None of it is PHP2Shell because it all predates the disclosure. It is the Internet’s current affairs’ noise, and that noise is why I do not leave PHP patching to chance. A fair caveat: an IP location shows where a connection from, not where a person sits, and three of these resolve to Google Cloud servers. If its a bot, it is pretty obvious, but if its a human, it could be an AI agent at the behest of its owner.
My Bots, Agents and Humans Probes List (End Sep – Oct 26)
What Claude Fable 5.1 and Opus 5.5 Can and Cannot Do
You may be wondering what the latest Claude models can hack, so here’s the short report. Claude was not among the models Wiz credited in the PHP2Shell research, so I will not attach this story to Anthropic. What Anthropic has published is that Claude Fable 5.1 and Mythos 5.1 are the same model with different safeguards, and its system card describes the strongest cyber capabilities of any model it has released. On general access, safeguards block or reroute offensive work such as reviewing source code for bugs remains permitted. Claude Opus 5.5 was released on 22 September 2026. It was described as comparable to Mythos 5.1 in cybersecurity and biology, and delivers with similar safeguards. Vetted defenders can get fewer restrictions through Anthropic’s Cyber Verification Program, which expanded into three tiers in October.
In layman’s terms, the capability exists and allows better access control rather than inability. Anthropic itself notes its safeguards have limits, and Wiz used other frontier models. The plan for a capable adversary, whichever the logo is found on the AI model.
Where AI Finds The Easy Wins
The PHP flaw is a deep engineering bug, but most real-world compromises still start with something boring. Wiz also showed that a related memory disclosure path could expose passwords, token, API keys, and certificates from a PHP worker’s memory, which is a reminder that your secrets are only as safe as the server they pass through. In my view, the weaknesses AI will exploit fastest are the ones we keep tolerating: unpatched software, passwords that are easy to guess or reused, encryption keys shorter than current guidance, and passkeys, or recovery methods synced across more devices, and accounts than anyone has audited. Passkeys are a genuine upgrade, but a passkey is only as safe as the weakest place it is stored. I covered how convincing AI-enabled fraud has become in my earlier piece on AI scams, and the lesson shows here. AI lowers the cost of attacking you, so the margin for carelessness and sloppy basic security practices are key fundamentals that facilitate these attacks.
What To Do Today
Start by finding your PHP version. In WordPress, go to Tools, then Site Health, then Info, then Server. Your host may already have patched, and some hosts backport the fix so the version number does not change. Verpex, for example, tells customers to check that the phpinfo() build date shows 21 October. If you manage your own server, update to a fixed version, and restart every PHP worker, as well as treat anything on PHP 8.1 or older as unsupported by the PHP project.
After patching, look for new web shells, unexpected scheduled tasks, and unfamiliar admin accounts, and consider rotating passwords and API keys your site has handled. Enterprises should add one more step, which is an inventory of every PHP install, including the ones hiding inside vendor software and appliances. Palo Alto Networks, for example, confirmed that all PAN-OS and Panorama versions are affected, and had not delivered fixed releases at the time of reporting. If your leadership team has not rehearsed this kind of crisis event, start with my guide to AI-assisted crisis communications for CEOs.
Check your host before attackers do
I host LadyinTechverse on Verpex, and during this incident the thing I valued most was transparency. Its status page logged the PHP update from 21 October. As of 22 October, it said patches were being rolled out for cPanel and Plesk shared hosting across PHP versions from 5.2 and above with no customer action required, Enhance panel sites were patched from PHP 7.4 and newer, and self-managed VPS owners were expected to apply vendor updates themselves. It also recommends moving to PHP 8.4 or newer if you are on 8.3 or older. The incident was still marked as recovering at the time of writing, so check the live page at status.verpex.com rather than trusting a blog post, including this one.
Disclosure: the link below is an affiliate link, and I may earn a commission at no extra cost to you.
Frequently Asked Questions (FAQs)
Is WordPress itself vulnerable to PHP2Shell?
The flaws are in PHP, not in WordPress, so WordPress.org says no WordPress update is required or planned. However, a WordPress site running on an unpatched PHP version is exposed, and Wiz demonstrated unauthenticated code execution against the latest official WordPress container image at the time of testing. The fix is a patched PHP build from your host, or server vendor.
Which PHP versions contain the fix?
PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35. The PHP project no longer issues security updates for 8.1 and earlier, although it has published minimal source backports for 7.4, 8.0, and 8.1 for teams that build from source. Some distributions, and long term support vendors also backport fixes, so ask your provider rather that assuming.
Is AI actively hacking websites through this flaw right now?
Exploitation attempts have been reported. Amazon’s honeypot network logged one on 17 October, before public disclosure, and watchTowr says it is observing attempts, while Huntress had not seen exploitation across its partner base as of 21 October. Researchers used AI to find and weaponise the flaws, and Huntress expects attackers to do the same, but attacker use of AI in this campaign has not been confirmed.
Can Claude Fable 5.1 or Opus 5.5 be used to hack a website?
Not on a general request. Anthropic says both deliver with safeguards that block or reroute most offensive cyber work, such as penetration testing and exploit generation, while ordinary secure-development work such as reviewing source code for bugs remains permitted. Vetted security teams can apply for reduced restrictions through the Cyber Verification Program. Safeguards have limits, so plan for capable adversaries using any model.
What should a small business do today?
Confirm your PHP version and patch status with your host, move to a supported PHP branch, and verify the patch rather than assuming it. Then check for unfamiliar files, scheduled tasks, and admin accounts, rotate credentials your site has handled, and use long unique passwords with two-factor authentication or passkeys you have audited.
Internal Articles
- AI Scams are Surging Fast | 2025
- How can CEOs use AI and Leadership to improve Crisis Communications in 2026?
- Own the Machine, Not the Model
- MCP went neutral. Five vendors Still Wrote the Rules.
- Why APAC B2B Senders are Losing the Inbox Placement Race
- 71% of AI Agent Traffic Hides Inside Your “Chrome” Analytics
- 60% Read AI Summaries. Your Content Answers One Question.
- WordPress Core Web Vitals: Why the Paid Audit is Losing its Case
- Three Retrieval Failure Modes Behind Wrong AI Agent Citations
- No Laptop Needed: Publishing a WordPress Blog Entirely From a Phone
- AI Crawler Access Control: The GEO Decision CMOs Must Own
- Outcome-Based Pricing for Fractional Professionals in the AI Agent Era
- Why B2B Teams are Giving AI Search Its Own Budget Line in 2026
- Agentic AI Governance: What Singapore CMOs Must Build First
- The First-Party Data Imperative: Owned Audiences in the AI Search Era
- MarTech Stack Rationalisation: What AI-Native CRMs Mean for APAC B2B
- LLM SEO Training Data vs AI Retrieval: The B2B Visibility Gap
- Machine-Readable Authority: How AI Systems Decide Who To Recommend
- Why Some MarTech Stacks Still Cannot Talk To Your AI Agents in 2026
- Ungoverned MarTech: The Hidden Compliance Risk Behind AI-Built Tools
- Why B2B Marketing Attribution is Broken in the AI Search Era
- Marketing AI Readiness: How to Prepare Your B2B Team for Agentic AI
- AI Hallucination Brand Risk in Zero-Click World: The B2B Marketer’s Verification Guide for 2026
- Why B2B Marketing Attribution is Broken in the AI Search Era
- Generative Engine Optimisation: How to Get Cited by AI in 2026
- Answer Engine Optimisation: How B2B Brands in Singapore Get Cited in AI Search in 2026
- Synthetic Content, AI Influencers and the Fight for Authenticity in Marketing
- What is Retrieval-Augmented Generation (RAG)? A Business Guide to AI that Knows Your Data
- I Built an AI SEO Agent to Fix the Visibility Gap in AI Search
- From Server to Sanctuary: Building for Agents, Living for Real?
- Personal Brand Authority in 2026: The One Asset AI Cannot Copy
- Vibe Coding is Rewriting Digital Services: What Agencies, SaaS, and Marketers Must Do Next
- AI Coding Tools 2026 – How to Choose the Right One for Your Workflow
- Why Internal Linking is the Most Underrated SEO Strategy You are Probably Ignoring
- The AI Productivity Paradox in 2025
- Agentic AI in 2025: Ripples that Signal the 2026 Workflow Tsunami
- How Brands Build Human Trust in the Age of Agentic AI, Starting in 2026
- Digital Trust in 2025: Governance and Security Shaping the Next Economy
- Data Quality is the Power Move behind every winning AI Strategy in 2025
Sources Referenced
- WordPress.org — Critical PHP Security Release, October 2026
- Dark Reading — PHP2Shell Bugs Signal Red Alert, October 2026
- Wiz — PHP2Shell: AI uncovers critical RCE vulnerabilities, October 2026
- watchTowr — PHP2Shell Rapid Reaction, October 2026
- Huntress — Rapid Response: php2shell, October 2026
- Help Net Security — PHP2Shell patched, October 2026
- W3Techs — PHP usage statistics, October 2026
- Anthropic — Claude Fable 5.1 and Mythos 5.1, September 2026
- CSO Online — Cyber Verification Program expansion, October 2026
- Verpex — Status, October 2026
Visual Content Disclaimer: All images in this post are AI-generated except ‘My Bots, Agents and Humans Probes List (End Sep – Oct 26)’.
PHP2Shell: What AI Changed for WordPress
#LadyinTechverse #DigitalSanctuary #MarketingTransformation #MarTech #PHP2Shell #WordPressSecurity #AISecurity #CyberSecurity #PHP #CMO


Leave a Reply